
How Northern Arizona Healthcare Cut Assessment Time to One Week and Strengthened Operational Resilience
Healthcare organizations manage risk across an increasingly interconnected ecosystem of vendors, products, technologies and operational dependencies. For health systems serving rural and remote communities, a technology disruption can have especially serious consequences. When critical systems become unavailable, transferring patients to another facility may not be an option.
Northern Arizona Healthcare has taken a proactive approach to managing these risks. Over the past year, the organization has reduced vendor risk assessment turnaround from more than a month to approximately one week, replaced ad hoc vendor assessments with a standardized process for new and renewing vendors, and embedded third-party risk assessment as a required control in enterprise technology governance. Together, these improvements have enabled the organization to manage a more comprehensive third-party risk program without adding headcount.
The Organization and the Program
Northern Arizona Healthcare is the largest health system in northern Arizona, serving a region of more than 50,000 square miles. Northern Arizona Healthcare’s largest hospital, Flagstaff Medical Center, is the only state-designated Level 1 Trauma Center north of Phoenix, which shapes how the organization evaluates every technology dependency it takes on.
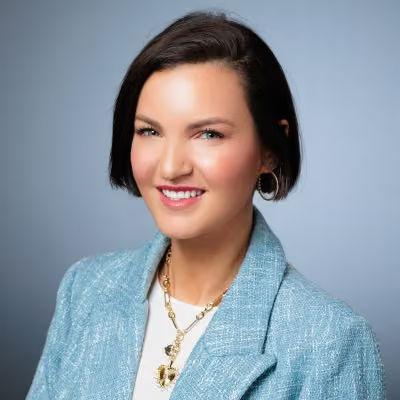
Sara Coverstone serves as Chief Compliance and Information Security Officer. A nurse by training who moved into compliance a decade ago, she leads a combined function that spans corporate compliance, privacy, audit, cybersecurity, data governance and AI governance. Three and a half years ago, the organization made a deliberate decision to move security out of IT and into that structure.
“It gave more executive and administrative support to cybersecurity across the organization. Cybersecurity had tended to compete for attention against the broader set of projects IT needed to complete.”
The Challenge: Manual Processes and Limited Risk Visibility
Like many health systems, Northern Arizona Healthcare managed third-party risk through processes that could not scale with a growing vendor ecosystem. Assessments were tracked on spreadsheets. Vendor contacts were identified individually, questionnaires were distributed by email, and every response required manual tracking and follow-up until it was returned.
The limitations compounded. Information was difficult to keep current and difficult to share consistently with IT and operational leaders who needed visibility into identified risks. Assessments were conducted as capacity allowed rather than as a standard requirement, which left the organization without a complete risk profile across its vendor ecosystem.
A related gap sat upstream. As in many health systems, individual departments could approve technology acquisitions before security or technology governance evaluated them. Without a required review, organizations can commit to products whose implementation requirements are not fully understood at the point of purchase.
The organization recognized early that scaling its third-party risk program would require a more consistent, efficient approach to risk assessments and governance.
The Evaluation: Three Requirements
Three requirements shaped the evaluation.
- A validated assessment framework. The team wanted confidence that its questionnaires were comprehensive without placing unnecessary demands on vendors. Standardized questionnaires that could be tailored to the organization's requirements would allow the team to adopt an established assessment framework rather than develop and validate one internally.
- Healthcare-specific expertise. Many controls are consistent across industries, but healthcare carries requirements and clinical context that general-purpose platforms may not adequately address. The organization wanted a partner that understood those nuances without needing them explained.
- Retained internal ownership. Cost considerations were important, and the team wanted a platform that would extend the capacity of its existing staff while keeping ownership of third-party risk management in-house.
“It makes a significant difference when the vendor understands the healthcare landscape. Many elements of cybersecurity are consistent regardless of environment, and many are unique to ours. Censinet knows what our pain points are, so we do not have to explain the nuanced differences.”
Onboarding
With Censinet RiskOps™, healthcare organizations can begin with an established library of healthcare-specific assessment questionnaires rather than spend months developing and validating their own. Purpose-built workflows, standardized risk scoring, and a structured approach to vendor and product risk management provide a foundation for immediate program activation.
Northern Arizona Healthcare began onboarding with support from its dedicated Censinet customer success team. Training began immediately, with the team moving into live assessments during onboarding. The first assessment was launched after the first day of training, followed by a second partway through the second day.
“It was really straightforward. We felt supported throughout, we had no concerns with how it went, and we would make the same decision again.”
The Impact
Assessment completion time reduced from more than one month to approximately one week
The Censinet Network connects healthcare delivery organizations with tens of thousands of vendors and products, enabling vendors to leverage previously completed assessment responses across multiple healthcare customers. Rather than answering the same questions from scratch for every organization, vendors can reuse their existing responses, reducing duplicative work and accelerating the assessment process.
For Northern Arizona Healthcare, this has significantly reduced the time spent coordinating assessments and following up on vendor responses. With vendors able to leverage their existing responses, the team can focus more attention on evaluating findings and addressing risks that warrant further investigation.
“The ability for vendors to leverage their previously completed assessment responses is enormously valuable. It is a significant time saver. We can minimize what we actually need to ask the vendor because they aren't starting from scratch each time.”
Assessment coverage expanded across the vendor ecosystem
Every vendor newly introduced to the organization now completes a security risk assessment. The program has since extended to existing vendors at renewal that had not been assessed previously. Alongside that assessment work, Censinet RiskOps™ continuously monitors 158 vendor organizations and 156 products across the ecosystem, giving the team visibility into 314 entities rather than only those most recently assessed.
“If you do not have a strong risk profile and an understanding of where your risks are, you cannot begin to mitigate them. Now we have the profile available to us on all of them, and can focus our efforts on figuring out where we need to take mitigation actions.”
Program capacity increased without adding headcount
A two-person team administers Censinet RiskOps™. Despite expanding the scope of its third-party risk program, Northern Arizona Healthcare has not added headcount. Instead, time previously spent on manual tracking and administrative tasks has been redirected to higher-value risk management initiatives the team could not previously undertake.
Third-party risk assessments embedded in technology governance
Working in partnership with the CIO, Coverstone helped design an enterprise technology governance process covering all new technology acquisitions. A single intake process now routes every request through a consistent review.
The legal team, which manages final contract review and signature, will not release a contract until the security risk assessment is complete.
This creates a deliberate control point, ensuring the organization evaluates potential product risks before making purchasing decisions rather than after.
More than 1,000 risk findings identified, with no high or critical risks left outstanding
Censinet RiskOps™ has identified 1,087 findings across Northern Arizona Healthcare's vendor and product ecosystem since onboarding. The organization has worked those findings to the point that no high or critical risk remains outstanding, demonstrating the value of not just identifying risk, but acting on it. Automated risk findings help the team prioritize which risks warrant attention without manually reviewing every questionnaire in full.
Secured funding for security investments by leveraging healthcare benchmark data
Northern Arizona Healthcare participates in Censinet's annual Healthcare Cybersecurity & AI Benchmarking Study. Unlike general cross-industry benchmarks, the study provides healthcare-specific comparisons that reflect the organization's operating environment. These insights have helped the organization identify areas for improvement and secure funding for security investments, including network segmentation.
“We have been able to draw straight lines to the benchmark results. We are able to point to a specific category where we would like to be more mature, and in order to be more mature, we have to improve our network segmentation, for example. Having healthcare-specific data is unparalleled. It is difficult to obtain benchmark data of that quality.”
Looking Ahead: AI Governance
Censinet AI Governance helps healthcare organizations assess and manage AI-related risks across their vendor and product ecosystem, combining structured assessments aligned to the NIST AI Risk Management Framework with systemic risk intelligence that can surface AI use in products already in operation. The need for greater visibility is clear. Censinet's 2026 Healthcare Cybersecurity & AI Benchmarking Study found that while 70 percent of healthcare organizations have an AI governance committee, only 30 percent maintain an enterprise-wide AI inventory, and 33 percent have no way to detect when a vendor embeds AI into an already-approved product.
Northern Arizona Healthcare operates separate data governance and AI governance committees, evaluating AI adoption from both technical and clinical perspectives. The organization has used its own AI questionnaire with vendors for several months and has now taken Censinet's AI assessment through its internal governance review, with adoption planned in the near term. Coverstone anticipates that AI-assisted summarization will deliver the most immediate value, by helping her team identify findings that warrant attention without reviewing every vendor response in full.
“I do not want vendors adding AI for the sake of AI. It needs to be meaningful. The intentionality Censinet has shown in making sure it is useful before releasing it has been significant for us.”
Why It Matters
For Northern Arizona Healthcare, cybersecurity is patient safety. The organization serves a region where the nearest alternative care facility can be hours away, raising the stakes of a breach or ransomware event involving a critical third party.
“We are the only Level 1 Trauma Center north of Phoenix, so we cannot easily divert patients. We have to care for patients despite the absence of computer systems and information. Without documentation, how do you verify a patient's allergies? How do you know you are giving them the right medication? It is life or death.”
The systems Coverstone describes rely on third-party technologies, as do the diagnostic platforms, pharmacy systems, transport dispatch tools and clinical applications the organization depends on every day. Assessing these products for security and privacy risk before they enter the environment and maintaining visibility into vendor breaches and ransomware incidents once they are in use helps Northern Arizona Healthcare identify and address risks that could disrupt patient care. This is why moving from ad hoc assessments to consistent risk oversight matters beyond efficiency.
Asked what she would tell a compliance or security leader still managing vendor risk through manual processes, Coverstone is direct.
“It is not sustainable, and it is not possible to be successful in the long run. We're all being asked to do more with fewer resources. Direct your resources to the areas where you can maximize their expertise, rather than manual entry on spreadsheets, so they can spend their time on the activities that actually address the risk.”
Healthcare Risk Intelligence in Practice
Northern Arizona Healthcare's experience demonstrates Healthcare Risk Intelligence™ in practice: using greater visibility into vendor and product risk to inform decisions and drive meaningful action. By expanding assessment coverage, strengthening risk oversight, and embedding third-party risk management into technology governance, the organization has built a more proactive approach to managing risks that could disrupt patient care.
The value is not simply in documenting risk, but in understanding what matters, prioritizing action, and strengthening operational resilience.
About Northern Arizona Healthcare
Northern Arizona Healthcare is a nonprofit health system that serves all patients regardless of their ability to pay. It is the largest health system in northern Arizona, covering a region of more than 50,000 square miles with a team of over 4,000 clinicians and staff serving more than 750,000 residents. The system operates two hospitals, Flagstaff Medical Center and Verde Valley Medical Center, with nearly 400 beds combined, and provides outpatient care through primary care, urgent care and specialty clinics across northern Arizona. Through Guardian Air Transport and Guardian Medical Transport, the system provides emergency transport services across 79,000 square miles. Its mission is improving health, healing people.
Censinet Impact
~ 1 week
314
1087
About Northern Arizona Healthcare
Northern Arizona Healthcare is a nonprofit health system that serves all patients regardless of their ability to pay. It is the largest health system in northern Arizona, covering a region of more than 50,000 square miles with a team of over 4,000 clinicians and staff serving more than 750,000 residents. The system operates two hospitals, Flagstaff Medical Center and Verde Valley Medical Center, with nearly 400 beds combined, and provides outpatient care through primary care, urgent care and specialty clinics across northern Arizona. Through Guardian Air Transport and Guardian Medical Transport, the system provides emergency transport services across 79,000 square miles. Its mission is improving health, healing people.
