
AI risk scoring is transforming healthcare by improving risk prediction, patient safety, and cybersecurity. Here's what you need to know:
- What It Is: AI risk scoring uses machine learning to analyze healthcare data, identifying risks faster and more accurately than manual methods.
- Why It Matters: It reduces preventable deaths (e.g., sepsis mortality down 17% at UC San Diego) and strengthens cybersecurity against rising threats.
- How It Works: By integrating data from sources like health records and medical devices, AI systems provide real-time insights for better decision-making.
- Challenges: Ethical concerns, bias, and regulatory compliance require careful oversight and transparency.
- Solutions: Tools like Censinet RiskOps™ simplify risk management with automated scoring, vendor assessments, and AI governance.
AI risk scoring doesn't replace human expertise - it complements it, enabling safer, more efficient healthcare systems while addressing emerging threats.
Responsible AI Governance in Healthcare with ComplyAssistant and McLendon IP

Key Components of AI-Driven Risk Scoring Models
Creating effective AI-driven risk scoring models for healthcare involves several interconnected elements. Each plays a crucial role in ensuring assessments are accurate, dependable, and secure.
Healthcare Data Integration
The foundation of AI risk scoring lies in securely combining various healthcare data sources. For instance, AI-powered medical devices can analyze a range of inputs, including single-lead ECG, SpO₂, heart rate, temperature, blood pressure, speech patterns, and even audio data like heart and lung sounds [3].
How Data Integration Works
AI models use methods like supervised learning, which relies on labeled datasets, and unsupervised learning, which identifies patterns in unlabeled data [3]. Public datasets, such as the MIT-BIH and PTB databases, are often used to train these models.
Ensuring Security and Compliance
Handling personal health information requires stringent security measures. Organizations must comply with regulations like HIPAA in the U.S. and the EU's General Data Protection Regulation for international operations. This involves encryption, access controls, and audit trails to protect sensitive data. Notably, the healthcare AI market, valued at $6.9 billion in 2021, is expected to grow to $67.4 billion by 2027 [3].
Once data is securely integrated, the focus shifts to developing and validating the AI models themselves.
Model Development and Validation
With integrated data in place, building reliable models becomes the next step. This phase focuses on creating systems that deliver accurate risk assessments while meeting industry standards.
Key Validation Techniques
Validation methods like cross-validation, holdout validation, and performance metrics help ensure models are reliable. Cross-validation, in particular, tests how well a model generalizes to unseen data [17, 19].
Overcoming Development Challenges
Challenges such as overfitting, poor data quality, and algorithmic bias must be addressed [4]. While accuracy rates of 70–90% are common benchmarks, metrics like precision, recall, and F1 scores provide a more complete picture [5]. Alarmingly, 44% of organizations have reported negative outcomes from inaccurate AI systems [6].
Best Practices for Success
Using diverse, representative datasets for training and validation is critical [4]. Explainable AI (XAI) techniques can make model outputs more understandable, and regular bias testing ensures fairness. Automated validation tools can speed up the process, and by 2026, synthetic data is expected to play a role in 75% of AI projects, offering new ways to train models while protecting privacy [6].
Continuous Learning and Adaptation
After validation, continuous learning ensures that models remain relevant. Unlike static tools, AI-driven systems adapt to new challenges and evolving healthcare needs.
Adapting in Real Time
AI systems improve their risk detection by learning from feedback and new data, allowing them to respond dynamically to emerging threats [7]. This real-time adaptability is critical in healthcare.
Self-Updating Algorithms
The trend is moving toward self-evolving algorithms that adjust automatically with minimal human input. These systems can counter new threats as they arise, including zero-day vulnerabilities [21, 22].
Maintaining Data Quality
For continuous learning to work, the incoming data must be reliable. Organizations need robust data pipelines to ensure a steady flow of high-quality information. Given that human error accounts for 68% of data breaches, adaptive AI systems are crucial in mitigating risks [7].
Static Scoring vs. AI-Enhanced Scoring
The gap here is operational, not just technical. Annual scoring can miss changes in exposure, access, and incident history that happen between reviews.
| Feature | Static Scoring | AI-Enhanced Scoring |
|---|---|---|
| Update Frequency | Annual or biannual assessments | Continuous, real-time ingestion |
| Data Variety | Primarily self-reported questionnaires | Questionnaires + telemetry + NLP-parsed documents |
| Scalability | Low; limited by analyst headcount | High; automates processing across thousands of vendors |
| Speed | Weeks to months per assessment | Minutes to hours for initial scoring, with rapid updates |
| Explainability | High (rule-based, traceable) | Variable; requires transparent features and documented thresholds |
| Monitoring Depth | Single review cycle | Longitudinal trend and anomaly detection |
Explainability matters because regulated teams need to trace every flag back to a documented feature, threshold, or control. That’s why explainable AI elements, such as transparent feature importance, documented thresholds, and alignment with frameworks like NIST AI RMF, are now treated as a governance requirement, not just a model design choice.
Ethics and Privacy Considerations
Ethical and privacy concerns are at the heart of deploying AI in healthcare. Addressing these issues is essential for building trust and maintaining compliance.
Tackling Bias and Ensuring Fairness
AI models can unintentionally reflect biases in their training data. Rigorous testing is necessary to identify and reduce these biases.
Transparency in Decision-Making
Healthcare professionals need clarity on how AI models arrive at their conclusions, especially when patient care is at stake. Explainable AI techniques can provide this transparency, fostering trust in the technology.
Safeguarding Patient Privacy
Protecting patient data is non-negotiable. Adopting privacy-by-design principles ensures AI systems work effectively without exposing sensitive information.
Balancing Human-AI Collaboration
Rather than replacing human expertise, AI should complement it. This partnership allows technology to enhance clinical decision-making while adhering to the ethical standards of healthcare.
Designing Scoring Models: Rules, Machine Learning, and Validation
Most healthcare programs end up with a hybrid model. Rules enforce the controls that can never be missing, and machine learning ranks risk among the vendors and systems that clear that baseline. Validation then decides whether people trust the output enough to act on it.
Rule-Based vs. Machine Learning Scoring
Use rules to enforce minimum controls. Use machine learning to rank vendors that already meet the baseline.
Rules are good for logic like "if PHI volume exceeds 500,000 records and the vendor lacks encryption at rest, assign high risk." That's stable, easy to explain, and doesn't need training data.
Machine learning helps when risk shows up as a mix of signals rather than one hard failure. For example, patching delays, rising external threat intelligence, and a recent minor incident may not trigger a rule on their own. Put together, though, they can point to higher future risk.
| Feature | Rule-Based Scoring | Machine Learning Scoring |
|---|---|---|
| Auditability | High; each flag traces to a documented rule | Moderate; requires feature documentation and threshold logging |
| Control Enforcement | Direct; rules block or escalate on specific control failures | Indirect; ML ranks residual risk after baseline controls are met |
| Maintenance Effort | High; rules need manual updates | Lower; adapts as new data arrives |
| Data Requirements | Specific, structured criteria | Large volumes of assessment and telemetry data |
Governance should then spell out who can override a score and how often the model is recalibrated.
Training, Validation, and False-Positive Control
The model is only as good as the features going into it. Useful inputs include the number of unresolved critical CVEs, average time to patch, whether MFA and network segmentation are in place, PHI volume handled, the count and severity of past incidents, and how much patient-critical work depends on that vendor.
Features tied to HIPAA safeguards, HITECH requirements, and FDA guidance for medical devices can improve the model's ability to surface vendors most likely to cause PHI exposure, clinical disruption, or device-related risk.
Labeled incident data is what makes a model predictive instead of just descriptive. In plain terms, that means records linking specific vendors to documented breaches, outages, or clinically relevant disruptions. Validation should use later incidents through time-based validation. Before deployment, clinical and security reviewers should also sample predictions to check that they line up with known incidents and disruptions.
False positives can wreck trust fast. If the model tags too many vendors as high risk, analysts start tuning it out. The fix is part technical, part operational: adjust decision thresholds with validation data, penalize missed high-risk vendors more than false alarms, and use tiered alerts so borderline cases get a light review instead of a full remediation cycle.
A few operating signals tell you whether the model is being taken seriously or ignored:
- Alert volume
- Time to review
- Analyst acceptance rates over time
Implementing AI Risk Scoring in Healthcare Organizations
Introducing AI risk scoring models into healthcare requires balancing innovation with accountability. For these systems to deliver meaningful outcomes, organizations must integrate them into existing workflows, adhere to regulatory standards, and encourage collaboration across teams. According to McKinsey, AI has the potential to save the U.S. healthcare system up to $360 billion annually by boosting efficiency and reducing adverse outcomes - a powerful incentive for getting implementation right [2].
Integration with Existing Workflows
The success of AI in healthcare depends on how well it's woven into current processes. To manage AI-related risks effectively, organizations need a structured risk management framework [2].
Starting with Pilot Projects and Ethical AI Development
Launching small-scale pilot projects can help ease staff into using AI, identify potential disruptions, and fine-tune systems before full deployment. Training algorithms on diverse datasets and conducting internal reviews are essential to ensure ethical AI practices, especially when diagnostic accuracy is on the line. For instance, Epic’s sepsis predictor faced criticism for generating excessive false alerts, leading to alert fatigue among medical staff [2].
Setting Clear Vendor Expectations
Healthcare organizations should demand transparency from AI vendors. This includes detailed documentation on data sources, validation methods, and performance metrics, ensuring alignment with ethical and regulatory standards.
Creating Backup Plans
To maintain uninterrupted care, establish contingency protocols for data access and alternative workflows. Incident reporting systems can also be implemented to track AI-related issues, offering insights for system updates and process improvements [2].
By integrating AI thoughtfully, organizations lay the groundwork for addressing regulatory and governance challenges.
Regulatory Compliance and Governance
Once workflows are optimized, the focus shifts to ensuring AI operations meet legal, ethical, and technical standards. Compliance spans several critical areas, including privacy, security, bias, transparency, and safety [10][11].
Developing Internal AI Compliance Frameworks
Organizations should define roles and responsibilities across the AI lifecycle. Assigning a compliance lead to monitor evolving laws and guidelines is a good first step [2][11]. The NIST AI Risk Management Framework can guide organizations in prioritizing governance, fairness, and transparency in their AI applications [9].
Maintaining Thorough Documentation
Clear records of data origins, model decisions, and risk evaluations are vital for meeting regulatory requirements. Audit trails, for example, help demonstrate compliance with HIPAA and other standards [11].
Collaborating with AI Compliance Experts
Specialists familiar with both technical systems and regulations can assist in integrating tools that explain model behavior, audit results, and test for bias [11]. Addressing bias is essential: one healthcare prediction algorithm, for example, was found to disadvantage Black patients by flagging only 18% for extra care, compared to the 47% who actually needed it. The algorithm had mistakenly used healthcare costs as a proxy for medical need [2].
Ongoing Monitoring and Auditing
Regular reviews, timely retraining of models, and staying informed about new laws and standards are key to maintaining compliance. Continuous monitoring helps organizations respond to emerging risks [8][11].
Team Collaboration
Strong collaboration across departments is the backbone of effective AI implementation. AI risk management benefits from a multidisciplinary approach that combines technical knowledge with insights from ethics, law, and social sciences [14].
Establishing Cross-Functional Governance
Creating a governance team with representatives from clinical, IT, legal, compliance, and ethics departments ensures a comprehensive approach to risk assessment. Tasks and findings should be shared with relevant stakeholders throughout the AI lifecycle [8][12].
Involving Stakeholders Early
Engaging clinicians, staff, and IT professionals early helps address concerns and align AI tools with actual workflow requirements [13].
Training Programs
Staff training is crucial for safe AI interaction and anomaly reporting. Emphasize that AI serves to enhance - not replace - human expertise [2][13].
Fostering an AI Awareness Culture
Building an organization-wide understanding of AI’s role in workflows can improve trust. Educating staff about decision-making processes and demonstrating how AI supports patient care are key steps [8][13].
"With ransomware growing more pervasive every day, and AI adoption outpacing our ability to manage it, healthcare organizations need faster and more effective solutions than ever before to protect care delivery from disruption." - Ed Gaudet, CEO and founder of Censinet [12]
Centralized Risk Management
A centralized AI risk dashboard can act as a hub for managing policies, risks, and tasks. This improves coordination among governance, risk, and compliance teams while offering a clear view of AI activities across the organization [12].
Currently, only 16% of health systems have a systemwide governance policy for AI usage and data access, highlighting the urgent need for robust frameworks [2].
sbb-itb-535baee
Human-in-the-Loop Review for High-Impact Decisions
AI should flag vendors and help rank them. It should not decide whether to end a contract or apply compensating controls to a system tied to direct patient care. For moves like that, human review is mandatory.
Escalation should kick in when a vendor supports direct care delivery, handles PHI, lacks recent evidence, shows conflicting questionnaire responses, or gets a score that could trigger a major remediation step. A qualified reviewer should check the evidence, document the decision, and record any exception.
AI can miss the messiness of day-to-day operations. That's why every high-impact decision needs a named owner, a review record, and an audit trail. When exception handling connects back to vendor tiering and remediation workflows, governance starts shaping action instead of just sitting on paper. It also helps teams handle edge cases the same way each time.
Adapting AI Risk Scoring Models to Changing Threats
Healthcare organizations are navigating an increasingly intricate cybersecurity environment, where threats evolve at a breakneck pace. With cybercrime costs projected to hit $10.5 trillion by 2025, growing at an annual rate of 15% [19], relying on static AI risk scoring models is no longer sufficient. To keep up, these models must embrace adaptability, building on the principles of continuous learning and rigorous validation discussed earlier. This ensures they remain effective as new threats emerge.
Updating Models with New Threat Intelligence
Keeping AI models up to date requires a structured and carefully verified approach to integrating fresh threat intelligence. This process ensures that updates enhance model performance without compromising security.
Ensuring Data Integrity and Security
The foundation of effective updates lies in sourcing data from reliable and trusted origins. Provenance tracking is critical here, allowing organizations to trace where data comes from and confirm its authenticity [16]. Cryptographic tools, such as checksums and digital signatures, can secure this data against tampering.
To stay ahead, healthcare organizations should also collaborate with reputable threat intelligence providers. These partnerships provide access to the latest threat data, which can then be filtered and applied to strengthen AI models.
Implementing Robust Verification Processes
Before incorporating new data, it’s crucial to thoroughly scan for vulnerabilities or hidden risks. This includes conducting vulnerability scans on model artifacts and closely analyzing data for any anomalies that might suggest manipulation or corruption.
Collaborative Intelligence Integration
Integrating threat intelligence effectively requires teamwork. Healthcare providers and device manufacturers should bring together experts from cybersecurity, regulatory affairs, engineering, and data science to validate new threat data before it’s applied [15]. Once verified, these updates can seamlessly integrate into monitoring systems, ensuring models remain both accurate and secure.
Monitoring and Evaluating Model Performance
Ongoing monitoring is key to ensuring that AI risk scoring models maintain their effectiveness. A strong monitoring strategy allows organizations to catch potential issues before they affect patient safety or data security.
Establishing Comprehensive Monitoring Systems
Continuous monitoring should include regular audits and detailed logging [16][17]. A dedicated governance structure can help standardize these practices across all AI systems, ensuring consistent oversight.
Performance Tracking and Analysis
System and user logs are invaluable for spotting unusual activity and tracking overall model performance [1]. Regular evaluations of clinical accuracy, security performance, and risk assessment capabilities can highlight areas for improvement. Additionally, routine vulnerability testing ensures that the models remain resilient against evolving threats.
Incident Response and Documentation
Organizations should have a clear AI incident response plan in place. This plan should outline steps to address performance issues, including procedures for switching to backup systems while investigations are underway [16].
Iterative Risk Assessment Processes
Given the ever-changing nature of cybersecurity threats, an iterative approach to risk assessment is essential. By continuously refining their processes, organizations can stay ahead of emerging risks.
Continuous Model Refinement
AI models must be regularly retrained and updated to address new challenges [18]. This involves incorporating fresh data, tweaking algorithms based on performance feedback, and learning from past security incidents. Research highlights the effectiveness of such strategies: organizations using AI have reported a 94% reduction in average detection time, a 75% drop in false positives, a 96% improvement in threat response speed, and a 70% decrease in undetected attacks [19].
Comprehensive Risk Mitigation Strategies
Effective risk management requires clearly defined roles and responsibilities [20]. Conducting thorough impact assessments and using a mix of risk evaluation techniques can help identify vulnerabilities before they are exploited. Regular assessments ensure AI models align with the organization’s overall security goals [1].
Flexibility in Process Design
To adapt to shifting requirements, iterative processes must be designed with flexibility in mind [19]. Systems should be able to quickly incorporate new threat intelligence, adjust to regulatory changes, and scale as the organization grows. Treating major updates as if they were entirely new models - by rigorously testing and evaluating them - can help prevent the introduction of new vulnerabilities while maintaining robust security measures.
Choosing an AI Risk Scoring Tool
Tools that produce AI risk scores vary widely in how well they fit healthcare. Use the criteria below to compare options, then roll the chosen tool out in stages.
Evaluation Criteria for U.S. Healthcare Organizations
Compare tools across eight areas that matter most in U.S. healthcare risk programs.
Healthcare alignment looks at whether a tool fits the day-to-day reality of care delivery. That includes vendor and product inventories shaped for healthcare, clinical vs. non-clinical classification, and critical-function mapping. If a tool can’t tell the difference between a clinical vendor and a non-clinical one, it’s not a strong fit for healthcare.
HIPAA and PHI coverage looks at how well a tool finds and scores risks linked to protected health information. Vendors that touch PHI should be tiered by actual exposure, not spend. A small vendor with access to clinical notes can create more risk than a much larger vendor with no PHI access at all [26][27].
Scoring transparency looks at how scores are produced and how clear the method is. Some tools create a pre-assessment inherent-risk score using structured factors, which gives teams a clearer starting point.
Continuous monitoring and evidence analysis were reviewed together because both help teams spot change between formal reviews. Tools score better here when they can automatically flag new breach activity, find embedded AI inside previously approved vendor products, and process SOC 2 reports or penetration test results without forcing staff to do all the work by hand.
Workflow automation and human review controls were also treated as a pair, not as competing ideas. Automation should cut repetitive work. But analysts still need the final say on high-stakes calls.
Reporting fit looks at whether outputs work for board, audit, and regulator reporting. Governance and privacy looks at audit trails, remediation routing, and isolated deployment environments. Those details matter because they shape whether a tool can be used in a way that’s defensible with regulators, not just useful inside the company.
A Phased Adoption Path
After you have a shortlist, match the tool to the stage your vendor risk program is in now. Most teams don’t build a polished program all at once. KPMG’s 2026 TPRM survey found that nearly half of respondents report only moderate automation maturity.[28] That’s a good reminder to take this in steps instead of trying to do everything at once.
Start with AI-assisted assessments. Get the basics under control before adding more layers. For many healthcare teams, that means moving off spreadsheets and into a healthcare-specific platform that standardizes questionnaires, uses AI to pre-score responses, and summarizes vendor evidence documents. This is the part where things stop feeling scattered.
Then move to continuous external monitoring. Once internal assessments are running in a steady way, add external threat scoring. Set clear thresholds upfront so your team knows when a lower external score should trigger a re-assessment or an escalation. Otherwise, the data just sits there and creates noise.
The next step is integrated AI governance and portfolio visibility. At this stage, define approval routing for high-risk vendor decisions and build dashboards that show concentration risk across your vendor portfolio. This gives leaders a clearer view of where risk is piling up, instead of forcing them to piece it together case by case.
Through all three stages, keep human approval in place for exceptions and high-risk decisions. That guardrail matters in healthcare, where one bad call can carry a long tail.
Case Study: Streamlining Risk Management with Censinet
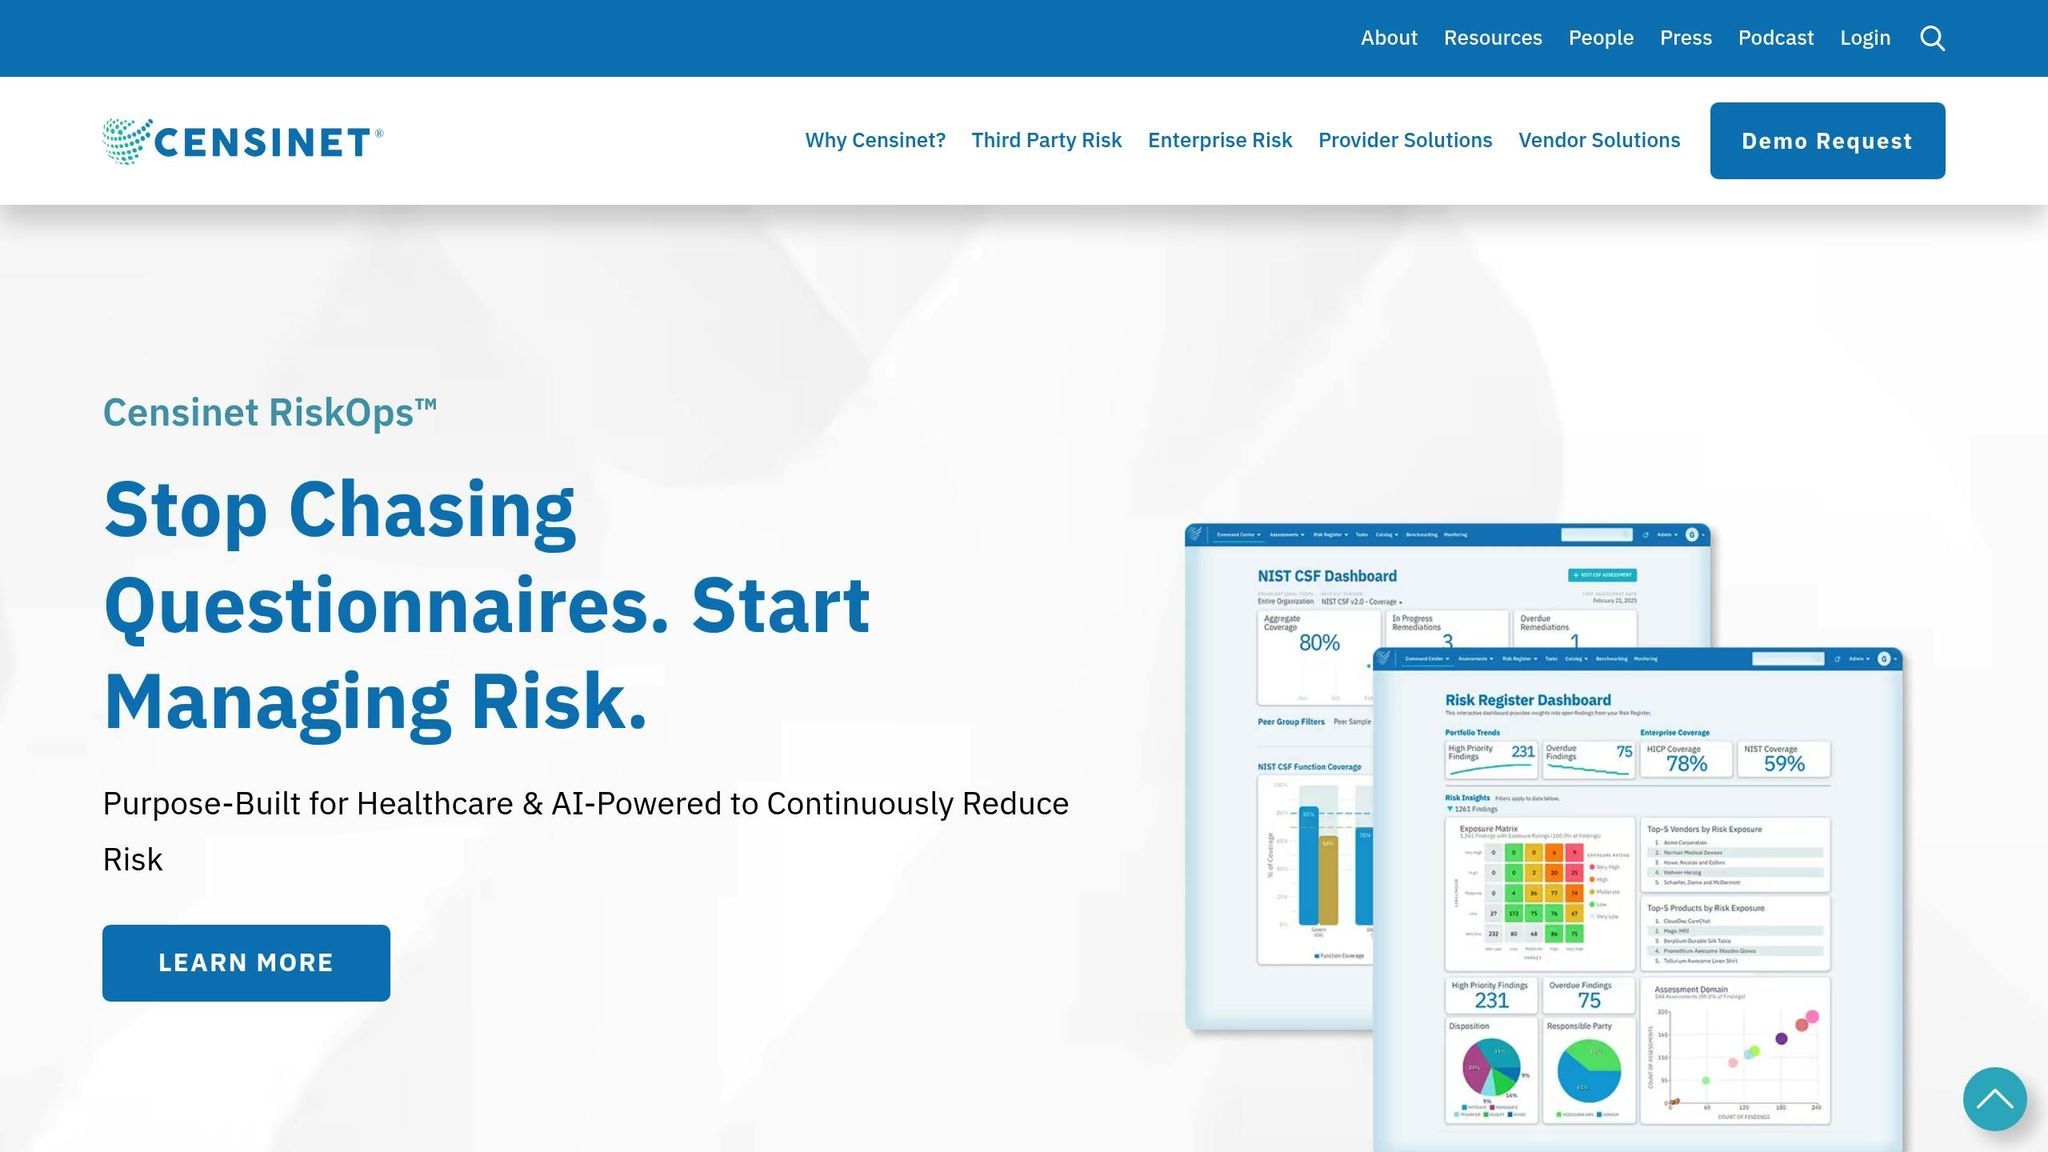
Healthcare organizations are under growing pressure to tackle cybersecurity risks while keeping operations running smoothly. This case study highlights how AI-powered tools, like Censinet RiskOps™, are reshaping traditional risk management strategies, offering practical solutions to meet these challenges head-on.
Censinet RiskOps™ Features and Advantages
Censinet RiskOps™ is a cloud-based platform designed to simplify enterprise risk management for healthcare organizations [21]. It reduces the time and effort typically required for assessments and reassessments, making the entire process more efficient.
Automated Risk Scoring and Assessment
Censinet's Digital Risk Catalog™ includes over 40,000 pre-assessed vendors and products [22]. Instead of starting assessments from scratch, healthcare organizations can tap into this extensive database, saving valuable time and resources.
Delta-Based Reassessment Technology
One standout feature is the platform's delta-based reassessment capability. This tool uses AI to pinpoint only the changes in vendor responses since the last assessment [22]. By focusing on these updates, organizations can complete reassessments in less than a day on average [22].
Integrated Risk Management Tools
The platform goes beyond basic assessments by offering features like breach alerts, automated risk tiering, and reassessment tools [22]. The Cybersecurity Data Room™ serves as a centralized hub for tracking and managing risks, while automated corrective action plans help address vulnerabilities systematically [22].
Standardized Vendor Assessments
Vendors benefit from standardized questionnaires they can complete once and share with multiple customers. This approach ensures consistency and streamlines the process for everyone involved [22].
Enhancing Collaboration and AI Governance
Censinet RiskOps™ also fosters better teamwork and oversight in risk management. It acts as a coordination hub for AI governance, ensuring that critical findings and tasks are directed to the right people for review and action.
Smart Task Routing
AI capabilities enable the platform to automatically assign specific risks and tasks to appropriate team members, including those on AI governance committees. This intelligent routing reduces delays and ensures nothing important slips through the cracks.
Centralized AI Risk Dashboard
A real-time AI risk dashboard aggregates data into a single, easy-to-navigate view. This unified perspective helps healthcare organizations monitor policies, risks, and tasks, allowing for quicker, more informed decisions across all risk management areas.
Human-in-the-Loop Integration
Censinet AI™ blends automation with human oversight at critical stages like evidence validation, policy creation, and risk mitigation. Configurable rules and review processes ensure that while automation handles routine tasks, humans retain control over key decisions.
Scaling Risk Management Safely and Efficiently
The platform addresses the challenge of scaling risk management without compromising safety or thoroughness. It aligns with broader strategies for tackling evolving threats in healthcare.
Balancing Automation with Oversight
By automating repetitive tasks, Censinet AI™ frees up risk teams to focus on complex decisions and strategic planning, all while maintaining essential human oversight.
Comprehensive Risk Coverage
From patient data to medical devices and supply chains, Censinet RiskOps™ provides a single, integrated solution to manage a wide range of cybersecurity risks.
Improved Speed and Efficiency
The platform accelerates risk management workflows, helping organizations respond faster without sacrificing accuracy or safety. This efficiency is crucial for maintaining patient safety and meeting regulatory demands.
Conclusion
AI-powered risk scoring is reshaping how healthcare approaches cybersecurity and operational risk management. By shifting from manual, reactive methods to intelligent, proactive systems, organizations can better protect patient data, improve operational efficiency, and cut costs across the board.
That said, ethical use and thorough oversight are non-negotiable. While AI offers impressive gains in accuracy and efficiency, history reminds us of its limitations. For instance, one healthcare prediction algorithm flagged only 18% of Black patients for additional care, and Epic's sepsis predictor missed 67% of cases while achieving just 63% overall accuracy [2]. These examples highlight why ethical implementation and explainable AI systems are essential.
Healthcare organizations must take concrete steps to ensure AI systems are used responsibly. This includes setting clear vendor criteria, training staff to understand AI's limitations, staying compliant with regulations, and creating contingency plans for potential system failures. The key to success lies in blending AI's capabilities with human judgment and ongoing oversight.
"Enterprise risk management in healthcare promotes a comprehensive framework for making risk management decisions which maximize value protection and creation by managing risk and uncertainty and their connections to total value."
The stakes have never been higher. In 2024, healthcare data breaches hit a record level, affecting 237,986,282 U.S. residents. Phishing-related breaches alone cost an average of $9.77 million per incident [24]. Traditional cybersecurity methods are no match for the complexity and scale of today’s threats.
Censinet RiskOps™ offers a way forward by combining AI automation with human oversight to streamline risk management. This approach, as demonstrated in the Censinet RiskOps™ case study, allows organizations to respond quickly and securely to emerging threats.
The future of healthcare risk management hinges on balancing AI's transformative potential with the ethical standards and human oversight that define quality care. John Riggi, National Advisor for Cybersecurity and Risk at the American Hospital Association, underscores this urgency:
"The Healthcare Cybersecurity Benchmarking Study plays a critical role in uniting the healthcare sector against a growing surge of cyber threats, enabling U.S. hospitals and health systems to better anticipate, withstand, and recover from cyberattacks through collaboration and data-driven insight." [25]
AI-driven risk scoring has the power to enhance efficiency and security, but it requires ethical implementation, continuous monitoring, and integrated platforms like Censinet RiskOps™ to truly make a difference. Healthcare organizations that take action now - by adopting these technologies, establishing strong governance, and investing in integrated systems - will lead the way toward a safer, more efficient, and patient-centered future.
FAQs
How does AI risk scoring improve patient safety in healthcare?
AI risk scoring plays a critical role in improving patient safety by analyzing diverse data sources like electronic health records and social factors. This approach delivers real-time, precise risk predictions, helping healthcare providers spot high-risk patients sooner. With this insight, they can act quickly to prevent adverse events, enhance diagnostic accuracy, and minimize avoidable harm.
By offering timely and focused interventions, AI-driven risk scoring empowers safer clinical decisions and contributes to better patient outcomes. Its streamlined risk assessment process allows healthcare teams to concentrate on providing effective, personalized care.
How do healthcare organizations ensure AI models are fair, unbiased, and compliant with regulations?
Healthcare organizations are actively working to make sure AI models are fair, impartial, and aligned with regulations. This involves tackling possible biases in the data, establishing solid data governance protocols, and following legal standards like the 1557 Final Rule, which aims to prevent discrimination.
Another key step is educating staff on AI ethics, transparency, and compliance. This training helps reduce risks and builds trust. By integrating these practices, healthcare providers can use AI responsibly, ensuring it promotes fairness and ethical care while staying within regulatory boundaries.
What are the best practices for integrating AI risk scoring systems into healthcare workflows?
To effectively incorporate AI risk scoring systems into healthcare workflows, it's essential to bring clinicians and other key stakeholders into the process from the start. Their insights help ensure the system aligns with clinical needs, delivers accurate results, and fits seamlessly into daily operations. This early collaboration can also minimize disruptions and encourage smoother adoption.
Equally important is establishing continuous monitoring and maintaining transparency about how the AI system works. These practices build trust among users and help ensure the system performs consistently over time. Regular updates, informed by user feedback and changing healthcare demands, are critical to keeping the system relevant and effective.
How accurate are AI vendor risk scores?
AI-driven vendor risk scores shouldn't be judged on accuracy alone. That can be misleading, especially when most vendors fall into the low-risk bucket.
A better way to judge performance is to look at precision, recall, and calibration. These metrics show whether the model is flagging high-risk vendors well, missing threats, or assigning probabilities that line up with what happens in practice.
AI can also stumble in gray areas or reflect bias in the data behind it. That's why human review still matters. People need to check the results, pressure-test the model's calls, and make the final risk decisions.
When should humans override an AI risk score?
Humans should override an AI risk score in high-stakes or high-risk situations. The same goes for exceptions, but only after checking the AI’s findings first.
That matters most when the case isn’t clean-cut - like when there are anomalies, gray areas in compliance rules, or moments that call for expert clinical or compliance judgment. In a human-in-the-loop model, AI helps move review and scoring along faster. But the risk team still makes the final call and can adjust decisions based on governance thresholds and oversight protocols.
What should a healthcare team automate first?
Start by looking at what you’re dealing with right now: how many vendors you have, the level of risk each one brings, and which compliance rules apply.
Then automate the basics that will save the most time first. That usually means:
- A central vendor inventory
- Vendor criticality categories, such as PHI access or clinical impact
- Repeat tasks like questionnaire distribution, evidence collection, and compliance report generation
This approach keeps things simple at the start and helps teams focus on the work that eats up time day after day.
